You turn on the tap to fill a glass of water. Behind that simple act are systems that control its treatment and supply—systems that artificial intelligence (AI) could make easier for hackers to attack.
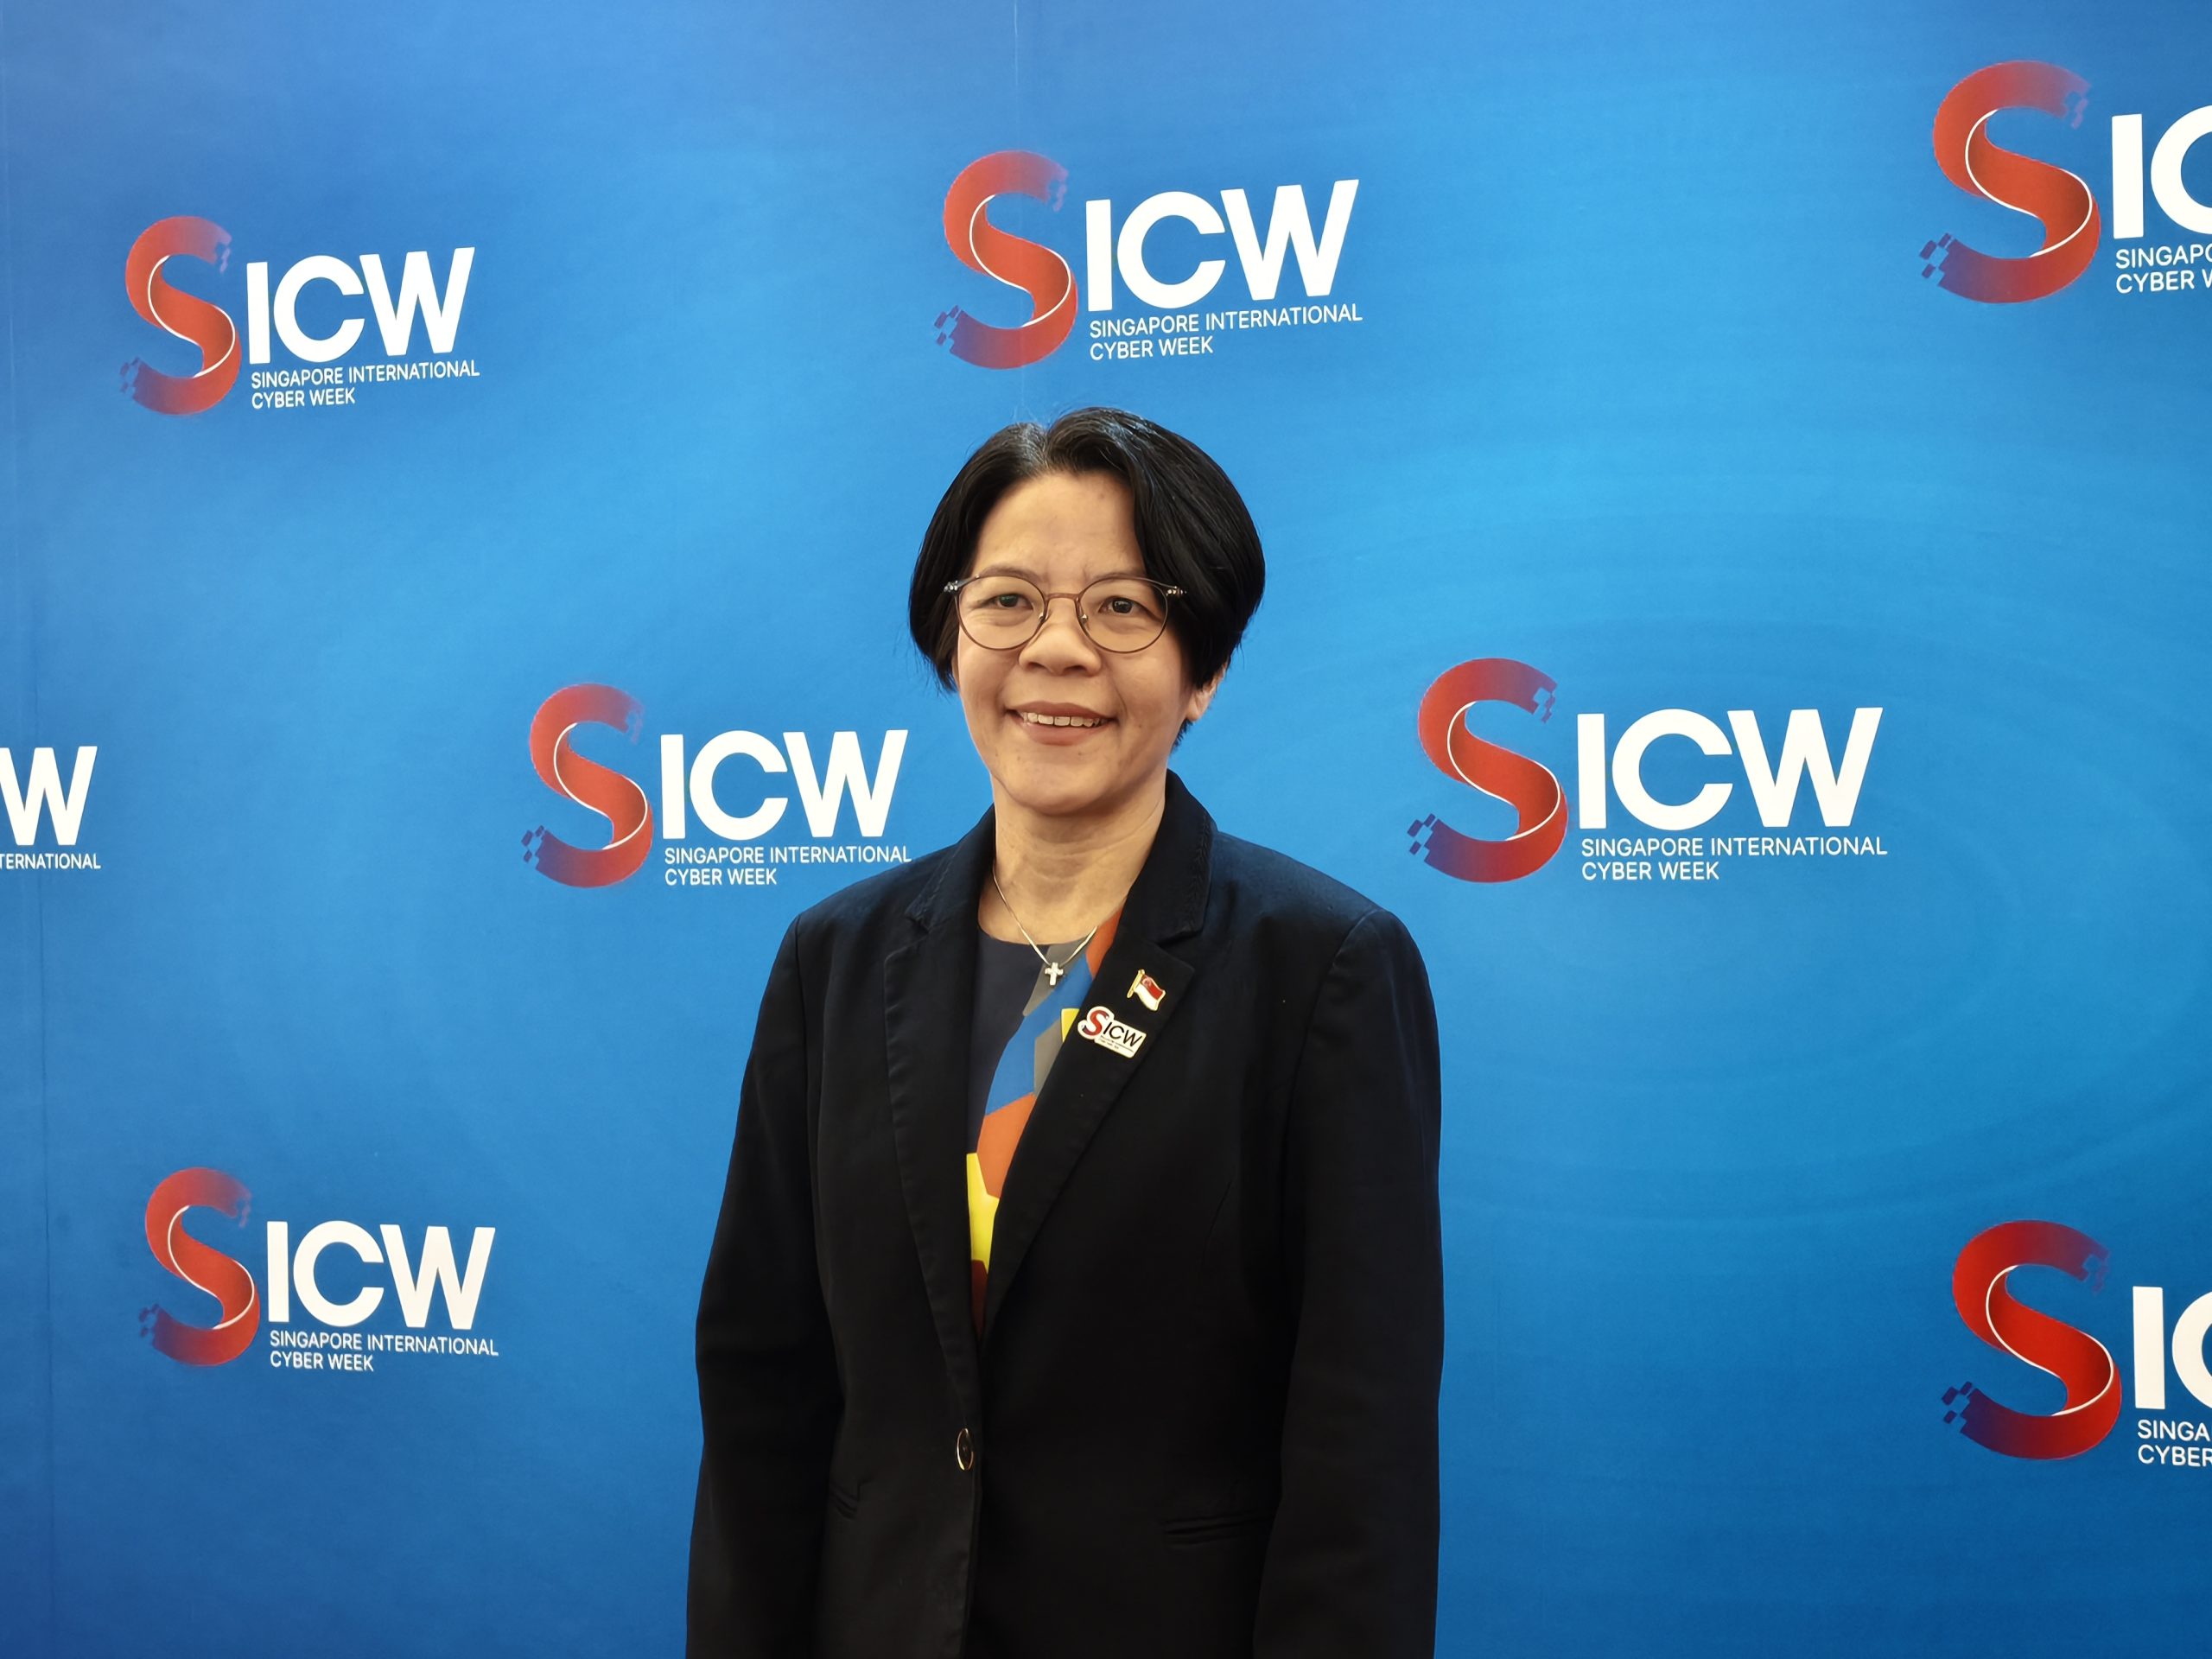
Gwenda Fong, chief executive of the Cyber Security Agency of Singapore (CSA), warned that AI could lower the level of specialized knowledge needed to attack operational technology (OT), which controls physical equipment and processes.
During a breakfast interview on the final day of Singapore International Cyber Week 2026, Fong said these systems had previously been less affected by cyber threats because of their specialized designs.
“It would take a lot of specialized knowledge to know how to attack an OT system,” she said.
AI, however, could help attackers read technical manuals and figure out how to target such systems, she added. More frequent attacks could affect the physical processes they control, bringing cybersecurity risks into everyday services.
“In theory, it could disrupt the distribution of water supply, or it could affect trains, it could have a more real-world impact,” Fong said.
The absence of visible disruption should not be taken as reassurance that such consequences will not occur, she added.
Fong took over as CSA chief executive and Singapore’s Commissioner of Cybersecurity on July 1, succeeding founding chief David Koh. She previously served at the agency from 2017 to 2022, helping draft and implement the Cybersecurity Act and update Singapore’s national cybersecurity strategy.
Keeping watch between security checks
For all the changes AI brings, Fong said basic cybersecurity measures remain essential. At the time of the interview, she said AI-driven attacks were still exploiting familiar weaknesses, including misconfigured systems and exposed networks, but at greater speed and scale.
Organizations must continue patching software, limiting exposure and separating networks to help contain breaches. They also need a clear inventory of their technology.
“You cannot protect or defend something that you don’t realize you have,” she said.
Speaking specifically about Singapore, Fong said some organizations still approached cybersecurity as a compliance exercise, relying on periodic assessments and reports.
The approach, she warned, is insufficient for an environment where attacks can develop rapidly. Organizations need continuous monitoring and visibility into activity within their networks, alongside measures to prevent intrusions.
The goal is to spot unusual behavior, investigate it and respond, rather than depend solely on scheduled security checks.
Preparing for a threat without a deadline
Beyond the immediate AI threat, Fong said governments and organizations must prepare for quantum computers becoming powerful enough to break encryption used today.
She described the two challenges as operating on different timelines. AI-fueled attacks already require attention, while the uncertainty surrounding quantum computing makes it harder to motivate organizations to commit resources to preparations.
“The challenge in not knowing exactly when Q-day is is you don’t quite know how much time you have,” Fong said, referring to the point when quantum computers could break existing encryption.
She compared the challenge to preparations for the Y2K computer problem, which had a fixed deadline at the turn of the millennium. The quantum threat has no similarly clear date, even though migrating to quantum-resistant systems takes time.
Singapore has begun discussions with critical infrastructure owners on plans to migrate their systems to quantum-safe encryption, she said. Organizations outside critical infrastructure that hold sensitive data should also begin preparing.
For Fong, strengthening defenses against current AI-fueled attacks must go alongside preparations for a less immediate threat. Given the time needed to address quantum risks, she said, those conversations need to begin now.
